Container Image Rebuild Failure Rates in GitHub Actions Workflows
Explicit cache keys and declared permissions prevent most container image rebuild failures.
Elise Cho
Explicit cache keys and declared permissions prevent most container image rebuild failures.
Compliance now runs on continuous signals, not annual paperwork snapshots.
Enterprise teams now see Nix's reproducibility as critical for security and compliance.
Rebuild-free deployments let teams prove what actually ran in production.
Gating deploys on manifest validation catches configuration errors before production breaks.
Five separate domains of trust shape a registry audit, not a single vulnerability scan.
AI agents reading operational artifacts need precise, structured data—not prose written for humans.
Malicious files in repositories can hijack AI coding agents through three hidden attack vectors.
Most CVE risk hides in transitive dependencies that traditional scanners never see.
Focus SCA evaluation on remediation speed, not detection count alone.
The 2026 CISA update replaces the 2021 baseline with 23 elements.
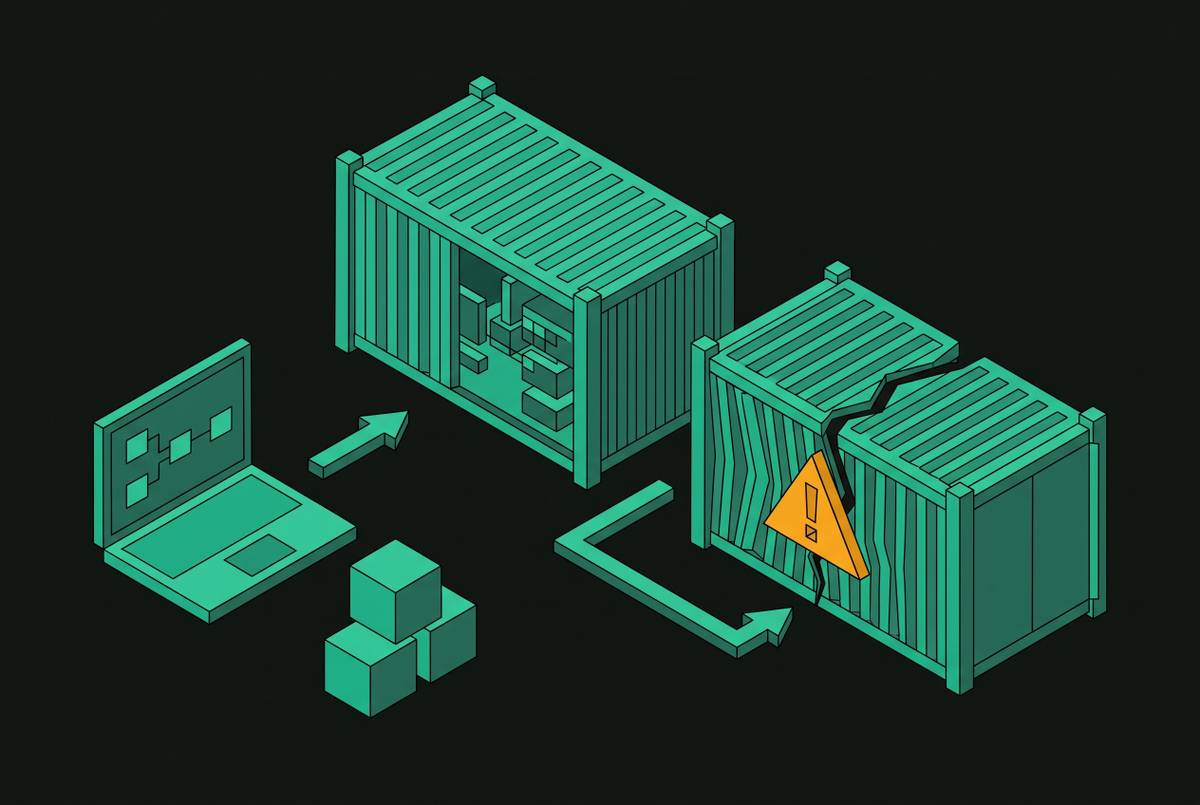
Stop container exploits before they spread across your cluster.